Email Security Blog

How Booking.com Impersonation Attacks Are Putting Hotels and Casinos at Risk of Credential Theft and Financial Fraud
Introduction Hospitality phishing campaigns targeting hotels, casinos, and travel-related operations Hotels, casinos, resorts, and travel operations rely on a constant flow of email messages to manage reservations, guest requests, payment questions, and partner communications. That volume creates the perfect cover...
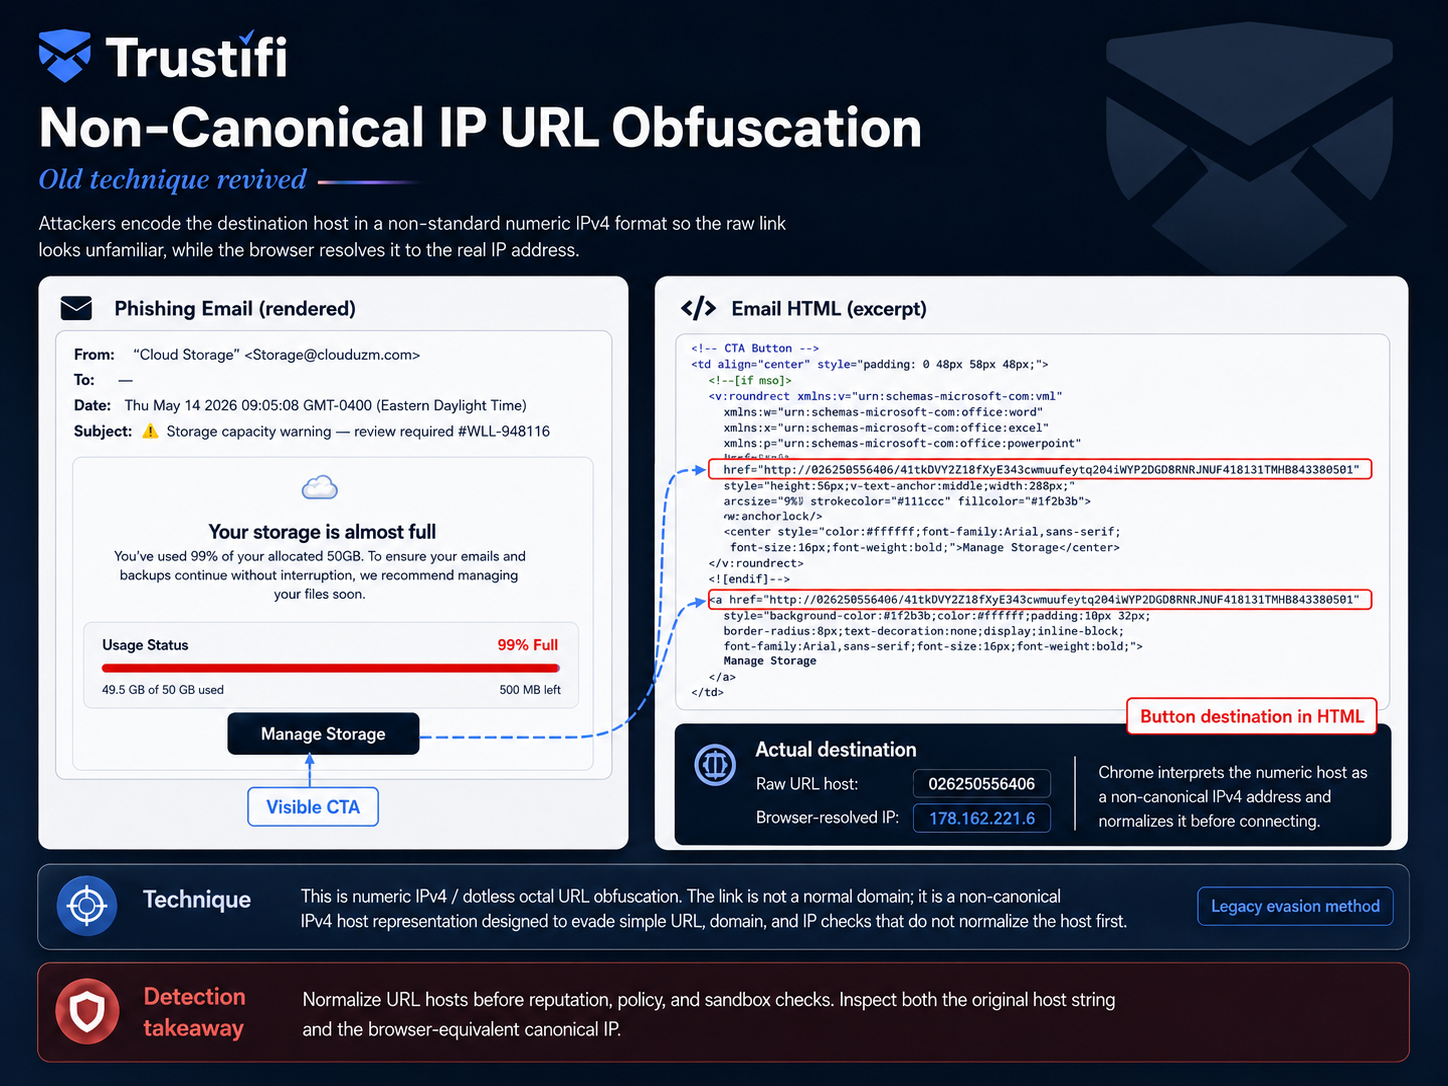
HostMimic: Old Technique Revived – Non-Canonical IP URL Obfuscation
HostMimic: Old Technique Revived – Non-Canonical IP URL Obfuscation Trustifi observed multiple quarantined phishing emails using a very old but still effective URL evasion technique: Non-Canonical IPv4 URL Obfuscation. We’re calling this observed phishing pattern HostMimic. The emails looked like...
Fake Claude Code Packages Are Stealing Developer Credentials, and Putting Enterprise Email Environments at Risk
Introduction Fake packages that imitate popular developer tools are becoming a serious risk, and Claude Code-related names are now part of that trend. Attackers use typosquatted package names, which are names designed to look almost correct, to trick developers into...
How AI-Powered Impersonation Is Fueling Phishing Attacks Against Public Sector Agencies
Introduction The rise of AI-generated impersonation in public sector phishing AI has made phishing more convincing, faster to produce, and easier to personalize at scale. Instead of sending generic scam messages full of spelling errors, attackers can now create polished...
How AI-Powered Law Firm Impersonation Scams Are Turning Legal Brands Into Email Fraud Weapons
Introduction The rise of AI-powered impersonation scams targeting the legal industry Law firms have always been attractive targets for cybercriminals, but AI has changed the scale and quality of the threat. Attackers can now generate convincing emails, fake legal notices,...
QR Code Phishing Is Surging in Microsoft 365: How Businesses Can Stop the Next Wave of Credential Theft
Introduction QR code phishing’s growing role in Microsoft 365 email attacks QR code phishing, often called quishing, has moved from a niche tactic to a mainstream email threat. Instead of asking a user to click a suspicious link, attackers place...
AI-Enabled Device Code Phishing: The New Microsoft 365 Credential Theft Threat Businesses Need to Stop
Introduction Overview of AI-enabled device code phishing Phishing has changed. In many Microsoft 365 attacks, criminals no longer need to steal a user’s password to get in. Instead, they trick the user into completing a legitimate device sign-in flow, then...
Why Business Email Compromise in Healthcare Is Now a Patient Safety Issue
Introduction The growing connection between cyber threats and patient safety in healthcare Cybersecurity in healthcare is no longer only an IT concern. When email systems are compromised, clinicians, administrators, billing teams, and vendors can all lose access to critical information,...
Microsoft 365 Under Attack: How AiTM Phishing via SharePoint Leads to Credential Theft and BEC
Introduction The rise of AiTM phishing in Microsoft 365 environments adversary-in-the-middle phishing, or AiTM , phishing has become one of the most effective ways to steal Microsoft 365 access. Instead of only collecting a username and password, these attacks can...